What's inside
SC-900 doesn't test whether you can list Microsoft security products. It tests whether you know what each security, identity and compliance capability is for, and which one fits a need.
This independent study guide for the Microsoft Certified: Security, Compliance, and Identity Fundamentals exam distils what SC-900 really expects you to understand into clear definitions, comparisons and the traps that catch newcomers. It assumes no previous security experience and is written to the skills measured as of 21 October 2026.
Organised by technology
Ten chapters, each readable on its own and together covering all four SC-900 skill areas:
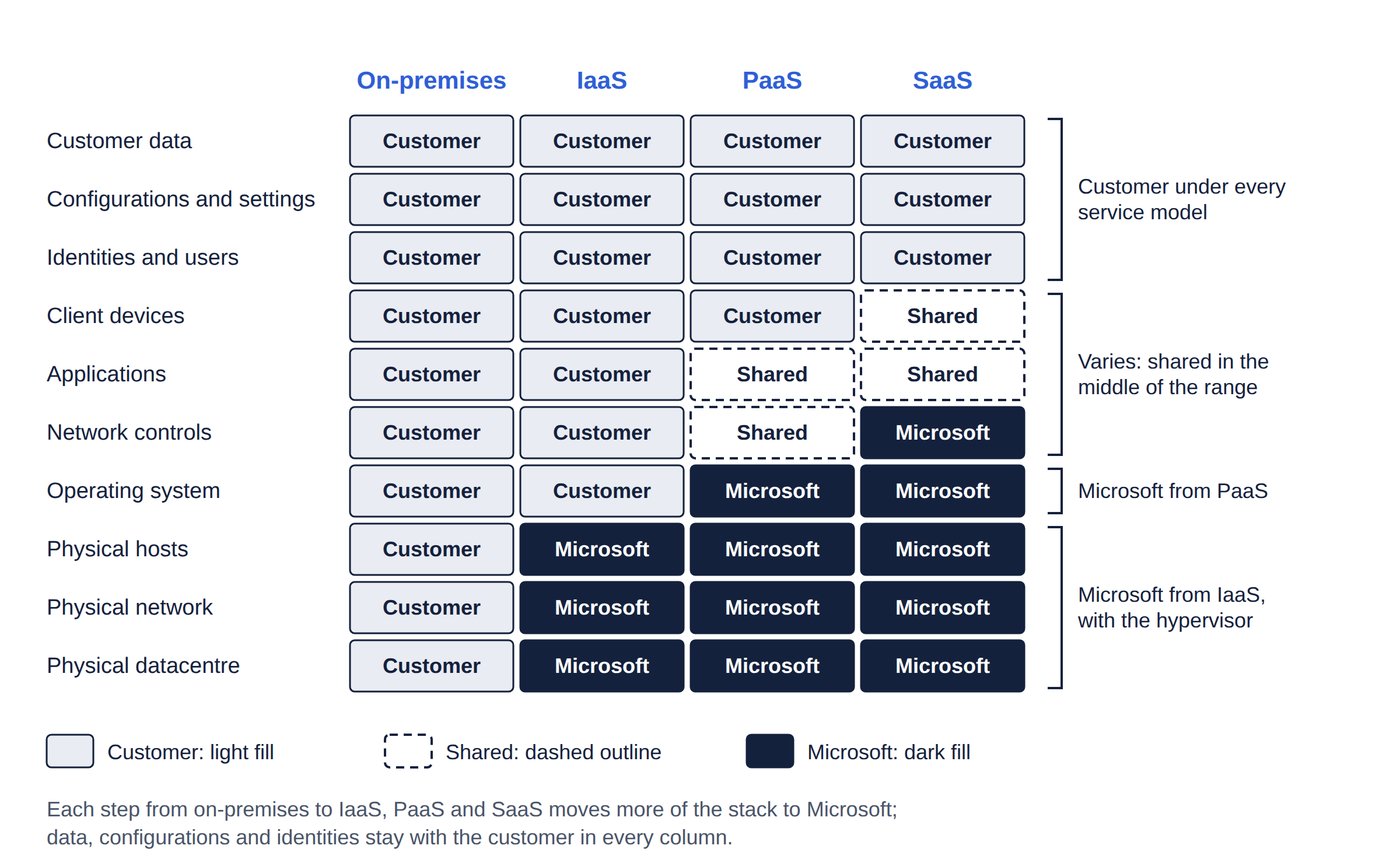
- Concepts: the shared responsibility model, defence in depth, Zero Trust, encryption and hashing, governance, risk and compliance, authentication, authorisation, identity providers, Active Directory and federation.
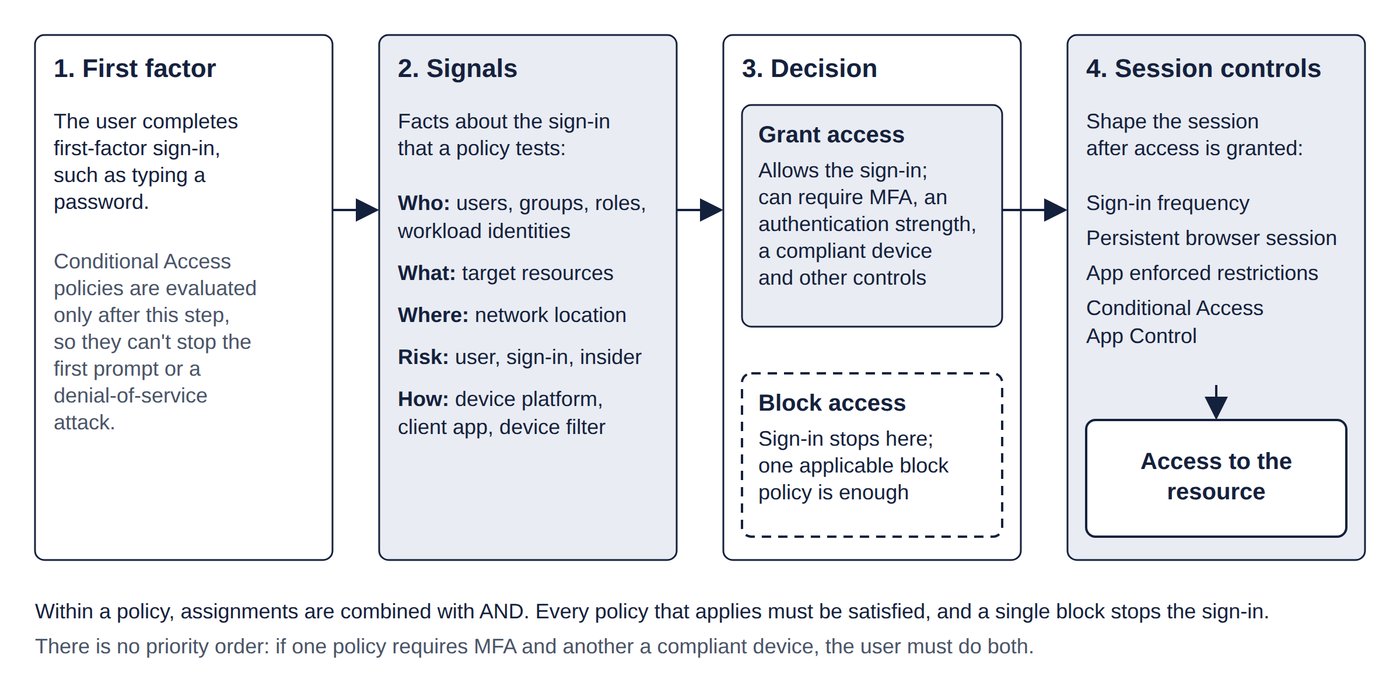
- Microsoft Entra: Entra ID, user, workload and device identities, hybrid identity, authentication methods, MFA, self-service password reset and password protection, Conditional Access, Entra roles and Azure RBAC, ID Governance, access reviews, Privileged Identity Management and ID Protection.
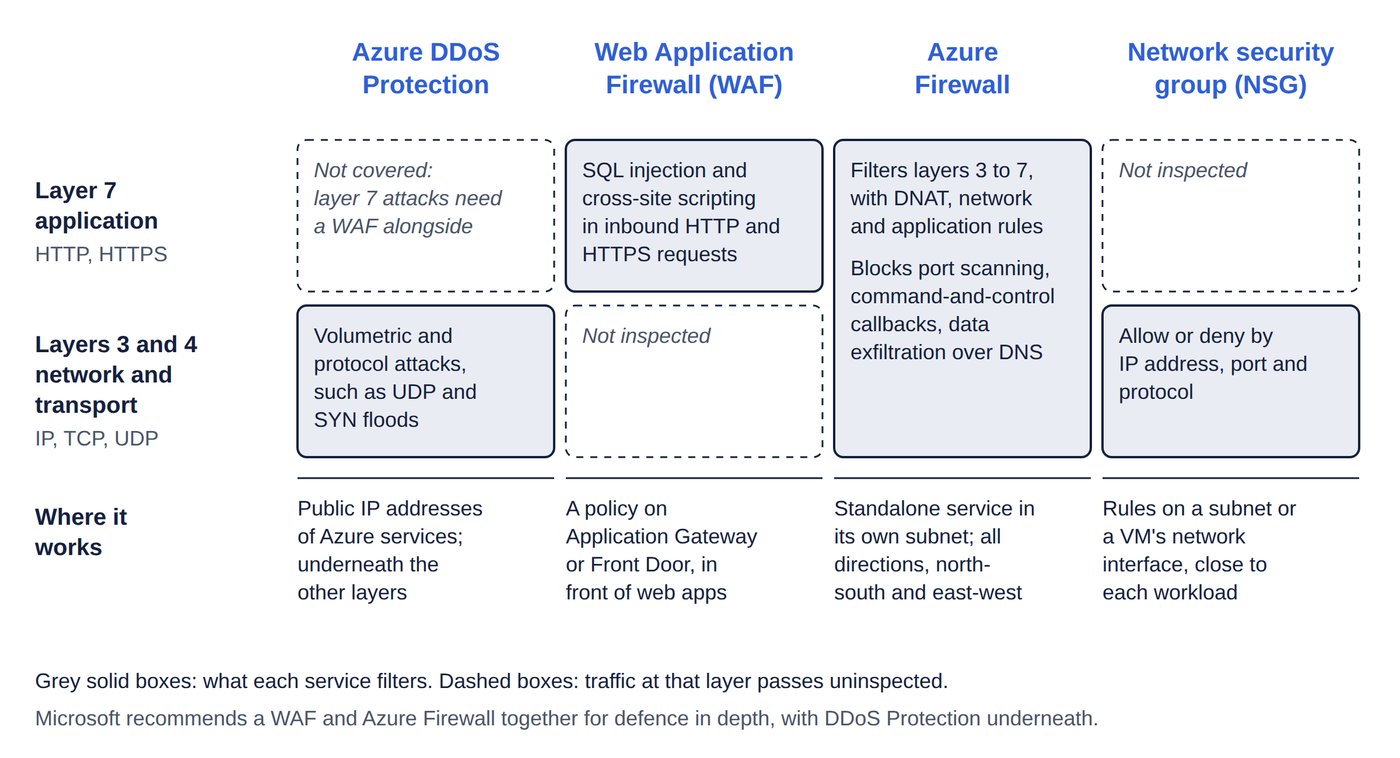
- Security solutions: Azure DDoS Protection, Azure Firewall, Web Application Firewall, network security groups, Azure Bastion and Key Vault; Microsoft Defender for Cloud, Microsoft Sentinel and Microsoft Defender XDR with Defender for Office 365, Endpoint, Cloud Apps and Identity.
- Compliance solutions: the Service Trust Portal, Microsoft's privacy principles, the Microsoft Purview portal, Compliance Manager, data classification, sensitivity labels, DLP, retention and records management, insider risk management, eDiscovery and audit.
Inside
- Comparison tables for every close call, such as which sign-in method, which network protection or which Defender plan fits a requirement.
- 70+ Common trap callouts that name the answers that look right but aren't, and explain what's right instead.
- 10 diagrams, from the shared responsibility model and Conditional Access to network protection layers and the principles of retention.
- Key takeaways at the end of every chapter for fast revision.
- A glossary of more than 300 terms, each linked to Microsoft Learn, with a free online version for print readers.
Up to date
Microsoft's security products change quickly. This edition reflects Microsoft's documentation as of October 2026, including recent changes such as the retirement of Microsoft-provided SMS and voice sign-in codes, passkeys by default, Microsoft Sentinel's move to the Microsoft Defender portal and the single eDiscovery experience in the Microsoft Purview portal.
Understanding, not memorising
This book contains no exam questions. It explains the knowledge the exam expects, so you can answer questions you have never seen and carry the same understanding into SC-500 and real security work.
Written by Tony Rough, a cloud architect with more than twenty years in IT infrastructure who holds the Azure Solutions Architect Expert, Azure Administrator and Azure Security Engineer certifications.
Part of the Ultra Transcenders series from Distilled Press. An independent publication, not affiliated with, sponsored by or endorsed by Microsoft Corporation.