An independent study guide for Microsoft Certified: Cloud and AI Security Engineer Associate · by Tony Rough
Know which control enforces it, and why.
Publishing soon on Amazon in Kindle and paperback editions.
Plus an appendix glossary of 800+ terms, each linked to Microsoft Learn, and free online for print readers.


Some sections of the book, free to read online:
How PIM activation, approval, maximum duration and notifications work, and what each role setting controls.
How a Conditional Access policy is built and how multiple policies combine.
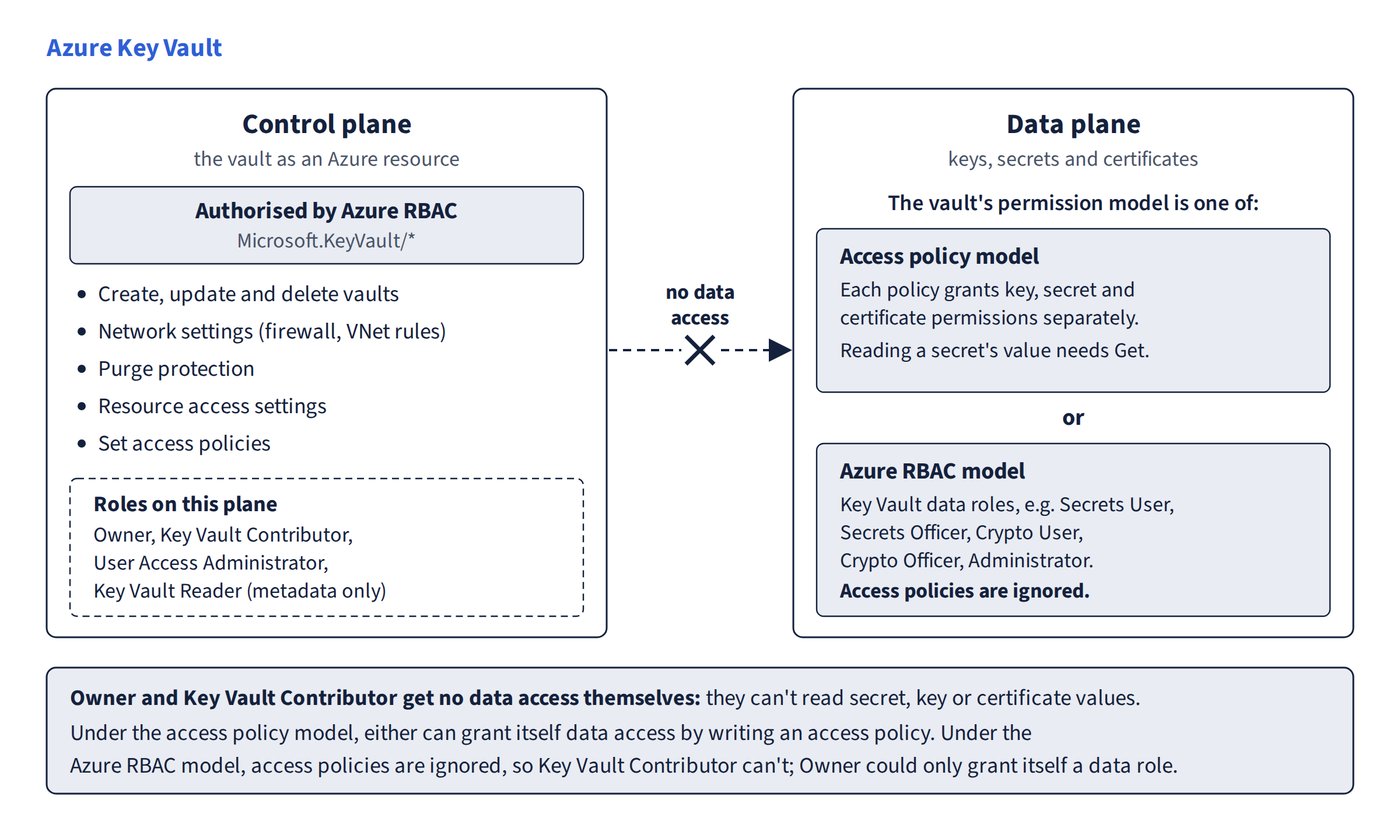
Why control-plane roles can't read secrets, and which Key Vault role or access policy each task needs.
What Deny, Audit, Append, Modify and DeployIfNotExists do, and when you need a remediation task and managed identity.
Account keys, account and service SAS, user delegation SAS and Entra RBAC compared by scope and revocability.
Where each Azure SQL data protection feature works and who it protects data from.
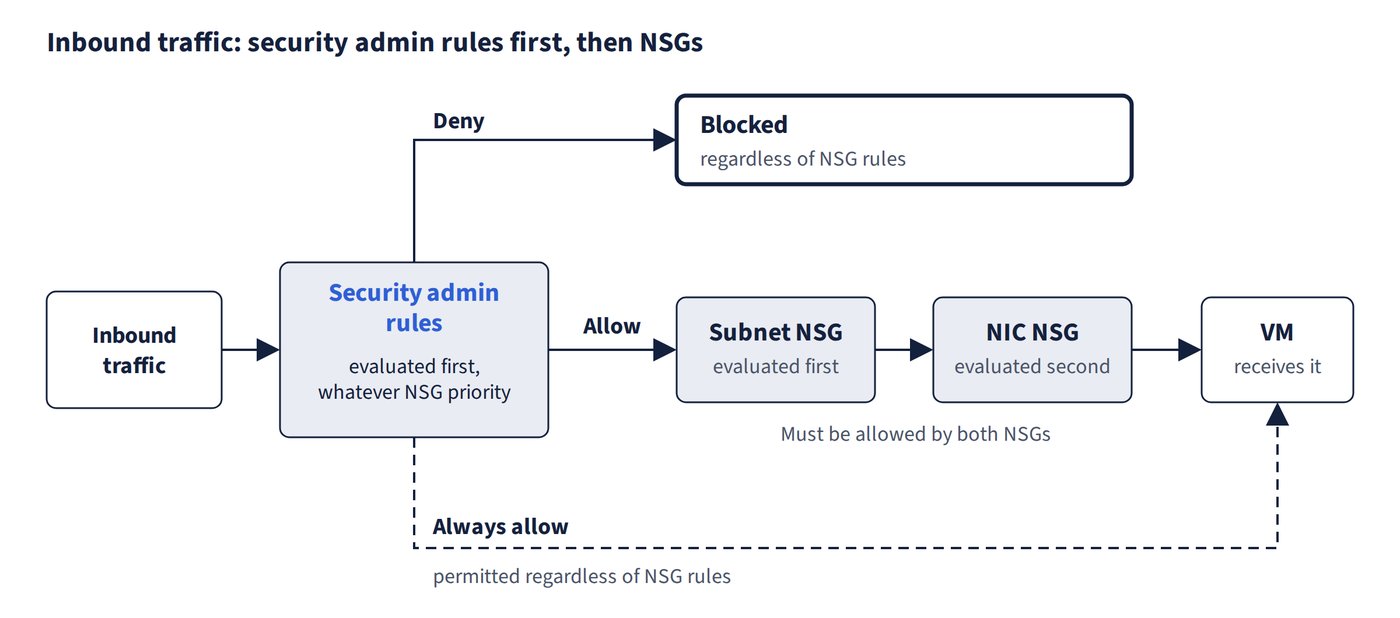
How security admin rules are evaluated before NSGs, and when to use Allow, Deny or Always allow.
How JIT locks management ports and opens them on request, with the plan and permissions it needs.